Without Cybernova Platform
Every alert starts from zero.
Teams move between tools, repeat the same checks and piece together a timeline while new alerts keep arriving.
 Lean AILabsRequest a walkthrough ↗
Bring security activity together, understand how events connect and give your team an evidence based view of what to review next.
Cybernova Platform connects the dots across company security signals so teams can spend less time sorting noise and more time understanding what is happening.
Teams move between tools, repeat the same checks and piece together a timeline while new alerts keep arriving.
AI agents triage, correlate and investigate together. Your team gets the evidence, a readable timeline and the next action to review.
Cybernova Platform works across hybrid and multi-cloud environments with your existing security stack. Its agents combine endpoint, network, cloud and identity context into one investigation your team can inspect, challenge and act on.
Meet the agent network →Connect signals from your SIEM and endpoint tools to build a more complete picture of each alert.
Link related activity across identities, endpoints and infrastructure into a single incident timeline.
Trace connected activity back to the earliest observed point to help identify likely patient zero, with supporting evidence visible.
Give your team a clear summary and recommended actions. They review and decide what happens next.
Bring supported Windows and Linux devices into investigations without requiring every machine to join your company domain. Cybernova’s specialist AI agents work in the platform, correlating available signals through access and sources your team configures.
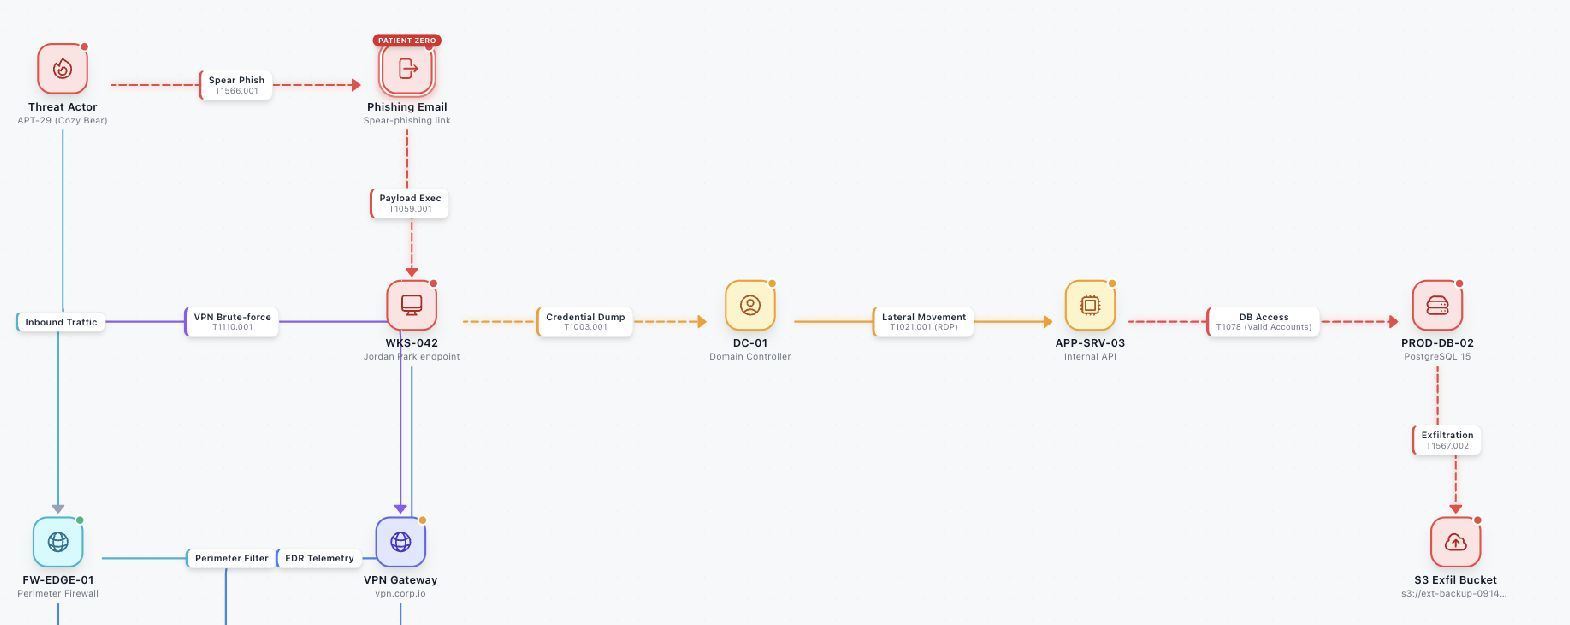
Cybernova Platform reconstructs how an incident may have started and spread. By connecting related events across the environment and tracing them back to the earliest observed activity, the Threatmap helps teams identify likely patient zero and review the evidence behind that assessment.
Let’s talk about your company’s security priorities and show you what Cybernova Platform can do.